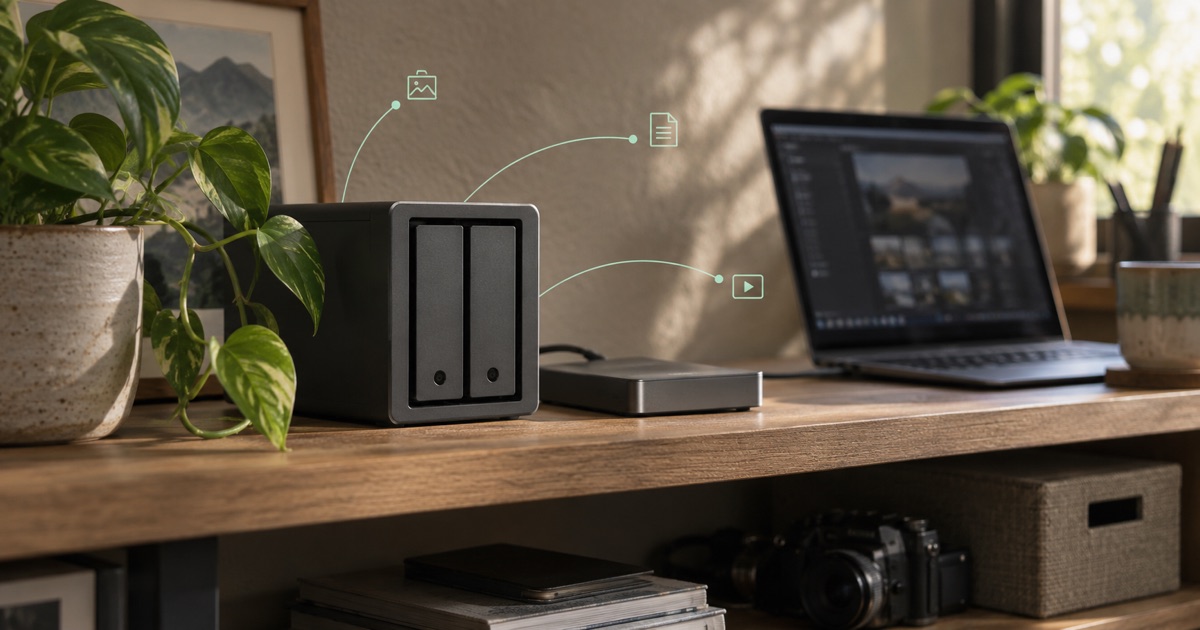
The design team needs a folder from home. The person maintaining the network-attached storage (NAS) device needs its administration page. The backup job needs a destination every night. These requests involve the same box but require different permissions.
For remote NAS access, define the shares and operations each audience needs, enforce them with NAS accounts, and connect approved clients through a supported private device or gateway path. Keep administration and backups separate from ordinary file access. A public port-forwarding rule is not required when private access meets the job.
Separate file-share, administrator and backup access
In a hypothetical studio, the NAS is 10.63.4.15. Designers need a Server Message Block (SMB) file share called Projects; the storage administrator needs a separate management service; a backup worker writes to a different share. The private address illustrates the layout and is not a configuration recommendation.
Record the actual protocols and ports for that NAS. A vendor’s browser administration page is not the file-sharing service, and the model’s defaults may differ from another model’s. Keep storage administration outside the ordinary designer grant.
The NAS also needs individual accounts and share permissions. If a designer should edit only Projects, the NAS must enforce that restriction. Network access to the storage host cannot tell the file server which directory a person may change. Avoid making every remote user a storage administrator to simplify setup.
Choose a joining method the equipment supports
A NAS that can run the required software in a supported environment may be a candidate for direct enrollment. Confirm the model, operating system, privileges and supported release. A package installation guide for a different device does not establish support for yours.
For equipment that cannot enroll directly, Fibmesh Networks can be assessed around a supported gateway and approved LAN resources. Check subnet overlap, local reachability and the return path before approving access. The NAS remains a downstream resource; connecting the gateway does not give the NAS a separate enrolled identity automatically.
A container on the NAS adds another network boundary. Verify that it can reach the intended storage service and that the required privileges and network behavior are supported. Do not assume a container, mobile device or arbitrary home router can act as a site gateway.
Compare supported device and gateway paths →Use an explicit share path when discovery is absent
A file browser may list nearby storage automatically at the office. That experience can depend on discovery traffic that does not cross a routed private path.
Use an explicit, approved hostname and share path in the remote test. Private workspace Domain Name System (DNS) records can make the name easier to maintain, but they do not create a broadcast domain or reproduce every vendor discovery feature. RFC 6762 defines multicast DNS around local-link naming, which helps explain why a discovery list and a routable service are different things.
If the share works by its explicit path but does not appear in a browser’s nearby-devices list, you have useful evidence: reachability may be working while discovery is absent. Do not widen the office subnet permission just to reproduce a browsing convenience.
Verify file-session encryption beyond the tunnel
The tunnel protects its supported transport legs. A final gateway-to-NAS LAN connection still needs an appropriate protocol security decision.
Check encryption support in the NAS and every intended client. For Windows file services, Microsoft’s SMB security guidance explains SMB encryption and its client/server prerequisites. That documentation does not certify every third-party NAS; use the model vendor’s guidance for its implementation.
Keep the management service protected with its supported encryption and authentication. Update the NAS and review unused services. A privately reachable device can still have vulnerable software or excessive permissions.
Test permitted and denied file operations
From an approved remote device, create a harmless test file in the permitted share, read it and remove it. If the intended use is read-only, verify that a write is denied instead. Check another share the user should not see and the management service they should not reach.
Use a representative transfer to understand the workflow on the actual home or mobile connection. Opening a folder is not evidence that a large editing project will behave well. Internet capacity, latency, file sizes and application locking still matter. Networks does not create storage replication or promise local-LAN performance.
Revisit backups separately. A remote path that lets the team edit files is not proof that backup jobs run or that restores work. Verify the backup account’s permissions and perform a small restore using the documented storage process.
Leave an owner beside the path
Record who maintains the NAS, who owns the gateway and who removes access when people leave. Give the team a supported recovery contact if the office connection or storage device is unavailable; do not assume automatic failover.
A useful first rollout is one share, one supported remote client and a clear administrator boundary. Once the permitted operation works and the unwanted operations are denied, extend the access map deliberately. The NAS can stay in the office while its remote access becomes something the team can explain, maintain and remove.